Template talk:Network Architecture: Difference between revisions
Jump to navigation
Jump to search
IVSWikiBlue (talk | contribs) No edit summary |
IVSWikiBlue (talk | contribs) No edit summary |
||
| Line 2: | Line 2: | ||
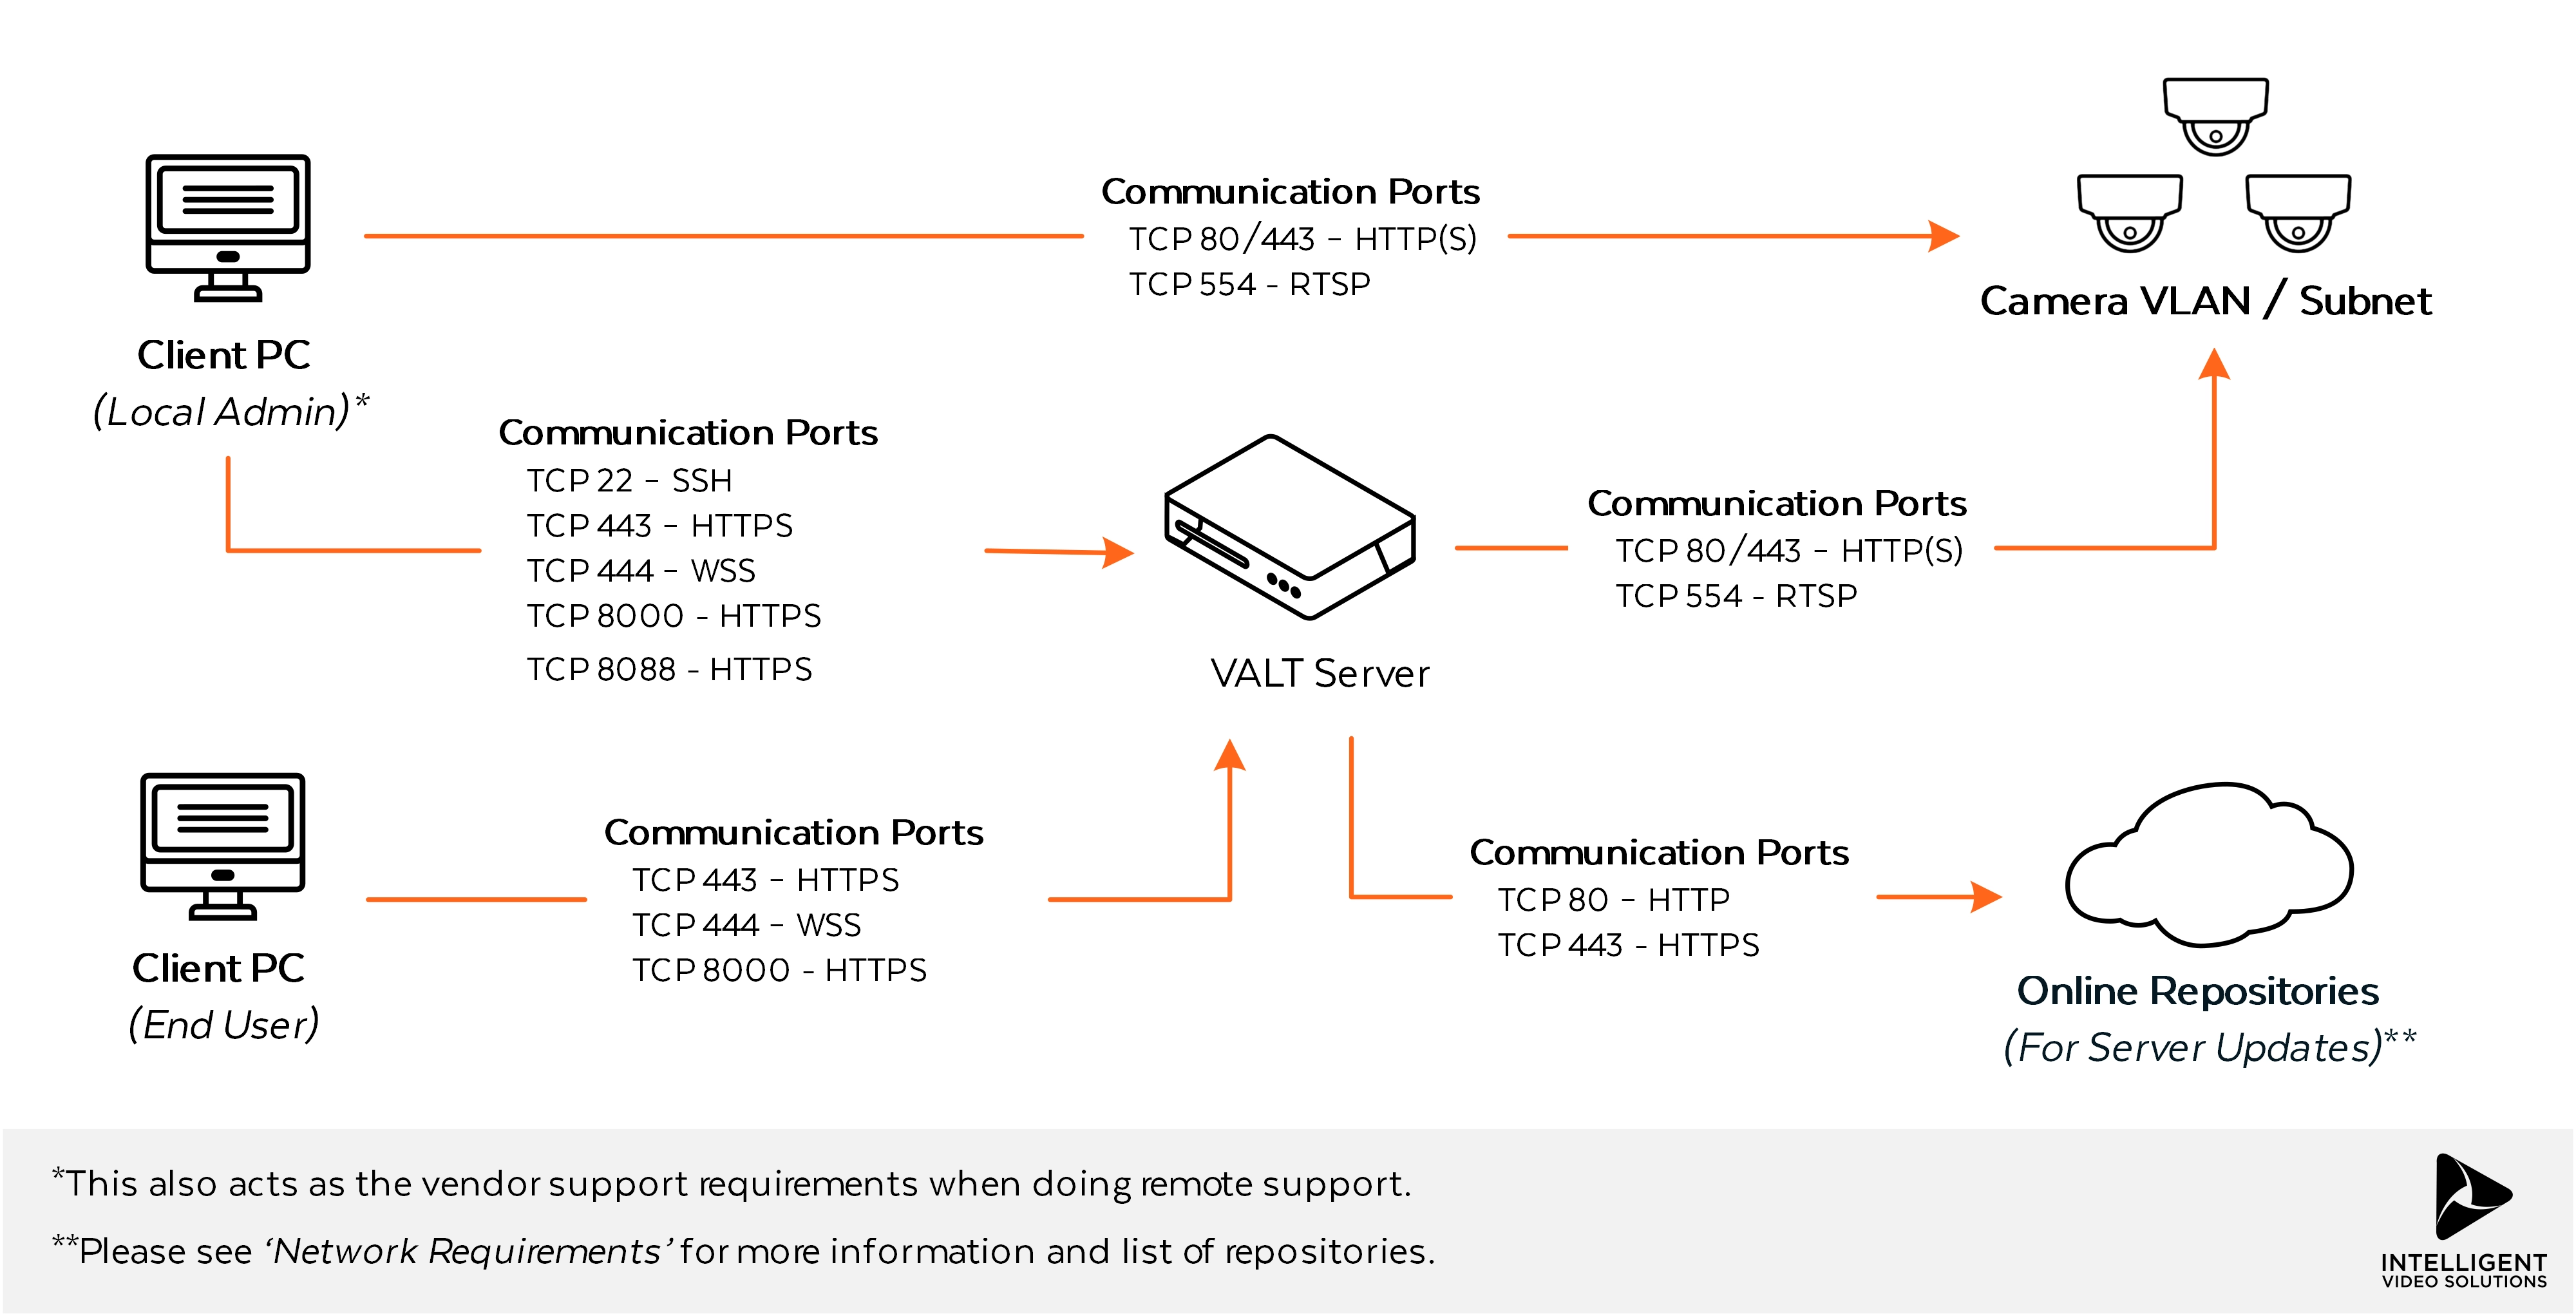
Below is a diagram of a sensitive network environment, where in-transit encryption is a requirement. This type of network architecture is typical of environments that are using the system to capture / observe actual patient interactions within clinical training environments. | Below is a diagram of a sensitive network environment, where in-transit encryption is a requirement. This type of network architecture is typical of environments that are using the system to capture / observe actual patient interactions within clinical training environments. | ||
{{img - resize| file = Network_testing_img.webp}} | {{img - resize| file = Network_testing_img.webp}} | ||
{{Aside | content = For SSL, we will need the customer to set up a DNS name for the server <em>(example ivs-valt.mysite.edu)</em>. We will also need a wildcard or generated signed certificate that is compatible with nginx and can be applied by an IVS engineer. LetsEncrypt may also be utilized.}} | {{Aside | content = For SSL, we will need the customer to set up a DNS name for the server <em>(example ivs-valt.mysite.edu)</em>. We will also need a wildcard or generated signed certificate that is compatible with nginx and can be applied by an IVS engineer. LetsEncrypt may also be utilized.}} | ||
}} | }} | ||
Revision as of 19:19, 23 January 2026
Below is a diagram of a sensitive network environment, where in-transit encryption is a requirement. This type of network architecture is typical of environments that are using the system to capture / observe actual patient interactions within clinical training environments.
✎
For SSL, we will need the customer to set up a DNS name for the server (example ivs-valt.mysite.edu). We will also need a wildcard or generated signed certificate that is compatible with nginx and can be applied by an IVS engineer. LetsEncrypt may also be utilized.