Authentication Workflows: Difference between revisions
Jump to navigation
Jump to search
IVSWikiBlue (talk | contribs) No edit summary |
IVSWikiBlue (talk | contribs) No edit summary |
||
| Line 28: | Line 28: | ||
<h2>SSO Authentication</h2> | <h2>SSO Authentication</h2> | ||
SSO accounts are automatically created when a user logs in for the first time. The user can be placed in the proper group automatically upon login by mapping SSO attributes to a user group within VALT. | SSO accounts are automatically created when a user logs in for the first time. The user can be placed in the proper group automatically upon login by mapping SSO attributes to a user group within VALT. | ||
<ul> | |||
<li>Users are assigned to groups each time they log in, based on the group membership attribute being passed</li> | |||
<li>If a user does NOT have a user mapping associated with their account, user gets moved to "Users without Group" and has restricted access</li> | |||
<li>If a user's user mapping changes, they will be moved to the correct group upon their next SSO sign-in</li> | |||
</ul> | |||
{{hr - 2}} | |||
{{img - no_click | file = SSO Flow Chart.png}} | {{img - no_click | file = SSO Flow Chart.png}} | ||
</onlyinclude> | </onlyinclude> | ||
}} | }} | ||
Revision as of 21:36, 27 March 2024
Authentication Workflows
There are three different authentication methods that can be used for VALT:
- Local Authentication
- LDAP Authentication
- SSO Authentication
Local Authentication
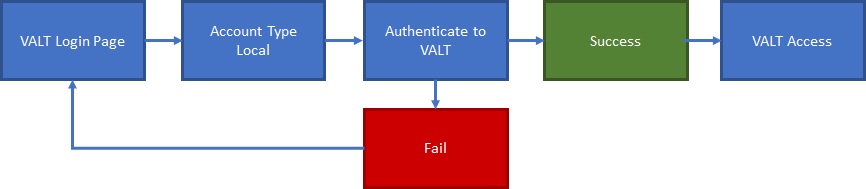
Local accounts are created and assigned to groups within VALT. Local accounts can be created manually or imported from a list.
LDAP Authentication
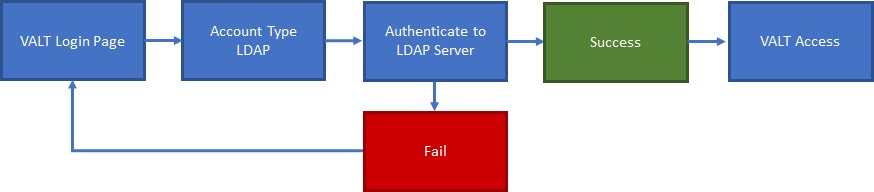
LDAP accounts can be imported manually using an LDAP search and lookup tool within the software or imported automatically on a schedule based on group.
SSO Authentication
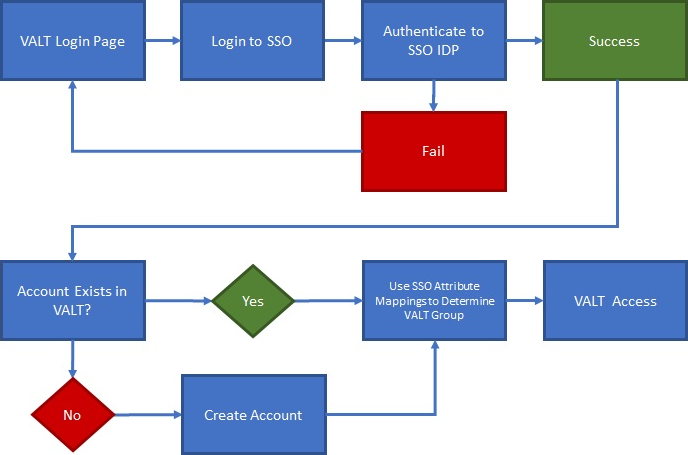
SSO accounts are automatically created when a user logs in for the first time. The user can be placed in the proper group automatically upon login by mapping SSO attributes to a user group within VALT.
- Users are assigned to groups each time they log in, based on the group membership attribute being passed
- If a user does NOT have a user mapping associated with their account, user gets moved to "Users without Group" and has restricted access
- If a user's user mapping changes, they will be moved to the correct group upon their next SSO sign-in